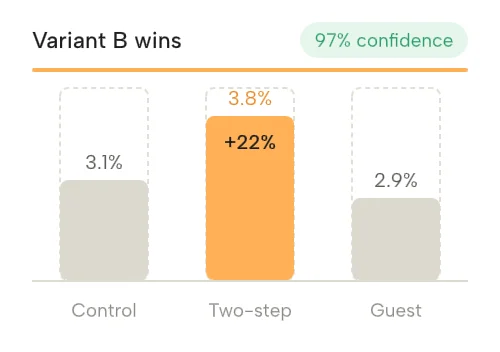


Kerf put every checkout change behind a flag and a test. We now know what works in days, and we ship twice as often.
Mei Tanaka
Head of Product
Kerf puts flags, experiments and AI analysis behind every release, so your team learns before it commits.
Kerf connects flags, tests, replays and analysis, so every release teaches you something.
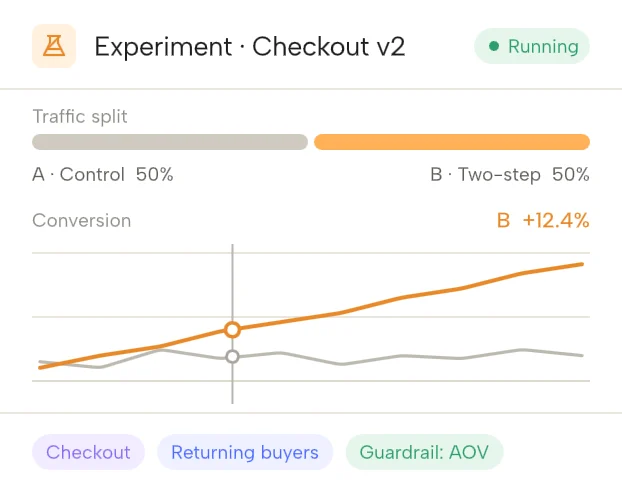
Roll out to any slice of your audience: plan, region, device, cohort or a list you upload. Kerf handles bucketing, exposure logging and holdouts.
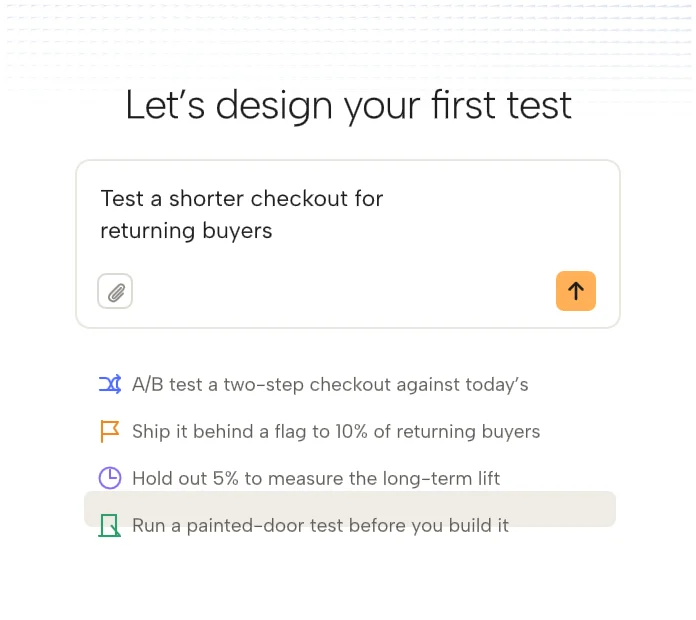
Write what you expect to change and why. Kerf turns it into a metric, a guardrail and a sample size before a line of code ships.
We take care of compliance and access, so your team can spend its time on the experiments that move the numbers.
Every flag evaluation, event and replay is encrypted with TLS 1.3 in transit and AES-256 at rest.
Decide who can create flags, launch tests and read results, down to a single project or environment.
Kerf is audited every year against SOC 2 Type II, and the report is ready for your security review.
EU data residency, a signed DPA and automatic PII masking in replays keep compliance simple. We never train models on your data.
Sign in through Okta, Entra ID or Google, and let SCIM add and remove people as your team changes.
Every flag flip, rollout change and test decision is recorded with who, what and when, and streams to your SIEM.
Kerf put every checkout change behind a flag and a test. We now know what works in days, and we ship twice as often.
Mei Tanaka
Head of Product
We asked 400 product teams how they decide what ships, and what changed when AI started writing the tests.